
DigiCert adds Secure Releases to Software Trust Manager
Wed, 28th Oct 2026 (Today)
DigiCert has added Secure Releases to its Software Trust Manager, linking release risk data with signing controls.
The feature is available in the product's Essentials, Advanced and Premium editions.
Secure Releases is intended to help organisations assess software risk both at the point of release and after shipment as new vulnerabilities emerge. It brings together information from supported GitHub releases, software bills of materials, known vulnerabilities, severity ratings and supported security scan results.
Teams can use that information to identify which software versions need attention and feed those findings into signing and release workflows. Users can also set requirements around vulnerabilities and SBOMs and, where supported, stop signing or release if those requirements are not met.
The move is aimed at a gap between code signing and ongoing software supply chain risk management. Code signing can confirm the source of software and whether it has been altered, but it does not show whether a component in a shipped release later becomes vulnerable.
That can leave security and development teams pulling together data from repositories, SBOMs, vulnerability databases and scanners to work out which versions are affected. Secure Releases groups that information by release so teams can track exposure and decide what action is needed.
Product scope
Under the new functionality, users can sign software and cryptographic inventories, including SBOMs and cryptographic bills of materials, or CBOMs. Recipients can then verify the source and integrity of those records.
The feature also supports signing other artefacts used in software assurance and compliance processes, including VEX statements, SLSA attestations, security evaluations and SARIF reports for customers and auditors.
The Essentials tier offers a point-in-time view of release risk. Advanced and Premium add ongoing monitoring of SBOM results by release as vulnerability information changes.
Premium includes additional controls. It can suggest a newer version of a vulnerable component when a fix is available and lets organisations block signing or release if software does not meet security requirements.
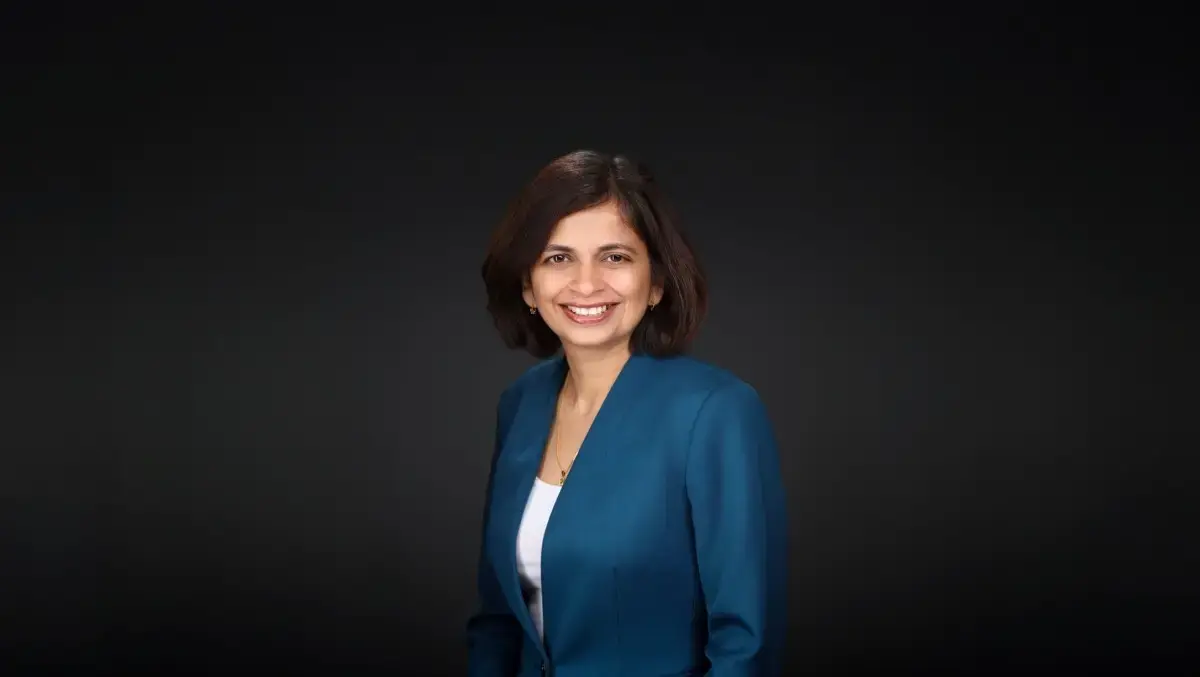
Deepika Chauhan, Chief Product Officer at DigiCert, outlined the rationale for the launch in a company statement. "Software signing proves where code came from and whether it has been altered, but those assurances do not tell teams whether a release contains a newly discovered vulnerability dependency," she said.
"Secure Releases brings those pieces together. By connecting release risk to the same policies that govern signing and delivery, organizations can respond faster when exposure changes and keep software from moving forward when it does not meet their requirements."
The new feature sits within DigiCert ONE, the company's broader platform for digital trust services. Software Trust Manager is designed to let organisations manage signing, release checks and supporting evidence in one system rather than across separate tools.
The focus on SBOMs reflects a wider shift in software security practices as customers, auditors and regulators seek clearer evidence of what is included in applications and whether known flaws have been addressed. Tools that tie that information to release controls are becoming more relevant as businesses try to trace the impact of vulnerabilities across multiple shipped versions.
DigiCert says more than 125,000 organisations use its products, including 90% of the Fortune 500.