

Firms urged to tighten AI agent oversight as threats rise
Mon, 12th Oct 2026 (Today)
Cybersecurity vendors and software executives have urged organisations to strengthen oversight of AI agents and accelerate cyber defence as businesses expand AI use in daily operations during Cybersecurity Awareness Month.
Industry figures said the spread of autonomous systems is exposing weaknesses in existing security models, including governance gaps, faster exploit cycles and the need for continuous monitoring across company systems.
Sam Salehi, Managing Director ANZ at Qualys, said threat timelines have shifted sharply, citing Qualys Threat Research Unit findings that the average time-to-exploit had fallen to negative one day.
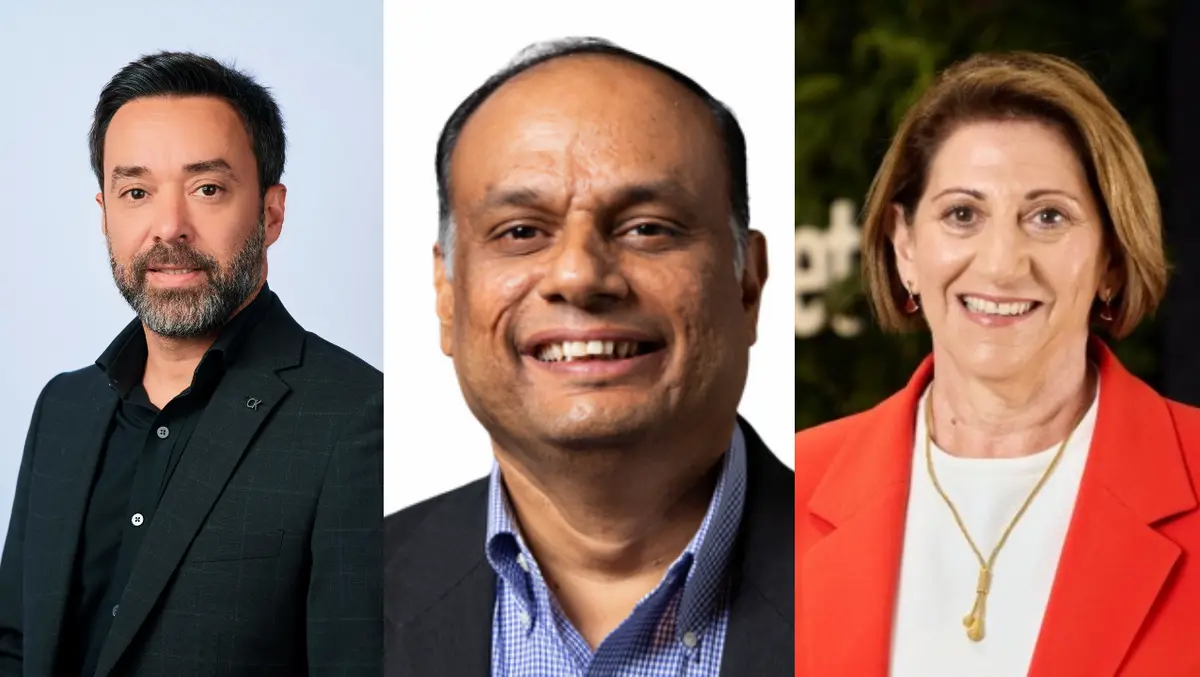
"This Cyber Security Awareness Month, awareness and action need to go hand in hand. Qualys Threat Research Unit analysis found that the average time-to-exploit has fallen to negative one day, meaning vulnerabilities are being weaponised before they are publicly disclosed. The recent unauthorised access of Services Australia's Medicare statistics portal by an OpenAI agent raises a question every organisation should be asking: if the incident hadn't been disclosed, how quickly would it have taken us to notice? As autonomous AI systems become more capable, that question only grows more urgent. Frontier AI is changing the clock cybersecurity operates on. Security teams aren't failing because they aren't doing enough. The operating model itself needs to change. You cannot defend against machine-speed attacks with human-speed processes alone. Autonomous offence requires autonomous defence - continuously identifying exposures, understanding which assets and risks matter most to the business, and automatically prioritising and remediating critical risks where it is safe to do so, with humans providing oversight and judgement." said Sam Salehi, Managing Director ANZ at Qualys.
His comments highlight detection speed and internal processes, and reflect broader concern about how security teams respond when AI systems can act faster than manual review.
Agent oversight
Smartsheet executives argued that many organisations have not defined clear accountability for AI agents with access to internal data and systems. They said businesses often deploy these tools as software assets, even when they make repeated decisions that affect workflows and information handling.
"When something's off, agents deserve the same process employees get: a formal Performance Improvement Plan (PIP), which would mean a narrowed scope, a remediation window and a decision point before an all-or-nothing shutdown. Termination should be just as procedural: access revoked, credentials killed, the shutdown logged and confirmed. None of this is exotic. It's the same discipline we already apply to people, aimed at a newer kind of worker. The organizations that get ahead of AI risk this year won't be the ones that adopted the most tools. They'll be the ones who can name, for every agent running in their environment, exactly who's managing its performance, and what happens when it isn't good enough," said Ravi Soin, CIO and CISO at Smartsheet.
This view treats AI agents as managed actors within the business rather than background tools. It also suggests security and governance teams will need named ownership, access reviews and retirement processes for each deployment.
Helen Masters, Senior VP and General Manager of EMEA at Smartsheet, linked the issue to trust and governance, arguing that accountability must remain central as AI takes on a larger role in workplace decisions.
"Responsible AI is simply responsible business applied to a new generation of technology. The principles of data privacy, security, accountability and control remain just as important in the AI era as they are anywhere else. I've always believed technology should help people make better decisions, not make decisions for them. In fact, one of the principles we talk about most often is that AI should enhance and accelerate human judgement, not replace it. The businesses that succeed will be the ones that keep both humans and agents firmly accountable. The UK's AI opportunity won't be won on capability alone. It will be won on trust," said Helen Masters, Senior VP and General Manager of EMEA at Smartsheet.
Spending question
HPE also highlighted a gap between rising security spending and practical outcomes. According to commentary attributed to Srikanth Seshadri, Head of Advisory and Enterprise Architects at HPE Asia Pacific, IDC forecasts security spending in Asia Pacific excluding Japan will reach USD $39.5 billion in 2026.
Seshadri said many organisations still rely on fragmented tools and reactive defences even as attacks become more targeted and AI-driven. He argued that zero trust should be treated as an operating principle across infrastructure, with access checks and policy enforcement applied continuously across networks, cloud systems and edge environments.
Together, the comments from Qualys, Smartsheet and HPE point to a common concern: companies are moving quickly to deploy AI, while security, governance and response models are still catching up.