

Flaw in Baltic PDF signature tools raises security fears
Wed, 18th Nov 2026 (Today)
Critical Security has found a flaw in four European digital signature tools that could allow unsigned pages to be added to a signed PDF while the software still shows the signature as valid.
The Lithuanian cybersecurity company identified the problem in Dokobit, GoSign, Latvia's eParakstītājs 3.0, and Estonia's SiVa validation service, along with the DigiDoc4 application that relies on it.
The weakness does not break the underlying cryptography behind electronic signatures. Instead, it stems from how some validation systems handle PDFs, which can legitimately accept later additions such as extra signatures or timestamps after the original document has been signed.
In the cases identified, the original signature remains mathematically valid, but the document shown on screen can include newer material not covered by that signature. Critical Security said that means a genuine signature could appear to endorse terms or pages the signer never saw.
The affected products are used across the Baltics and beyond. Dokobit is owned by digital identity company Signicat and is widely used in the Baltics and Iceland, while GoSign is operated by Lithuania's state-owned Centre of Registers.
The problem could be exploited with only a copy of a signed PDF, Critical Security said. An attacker would not need the signer's PINs, personal data or access to the electronic signature itself.
How It Works
A validation system should clearly warn users when part of the visible document is not covered by the signature, Critical Security said. Several popular systems failed to do that clearly enough.
Its account of the products' behaviour varies by service. Dokobit, it said, notes in a detailed report that the signature covers only part of the file, but its main summary still marks the document as valid.
GoSign, according to Critical Security, reports the document as properly signed while its preview displays the added page without a warning. eParakstītājs 3.0, SiVa and DigiDoc4 also return a valid result, it said.
Critical Security also said it found similar issues in systems in Portugal and other countries, though it did not identify those products.
All vendors were notified in October, according to the company. By November 11, it said, only the CERT.LV team had responded, saying the information had been forwarded to Latvian State Radio and Television Centre.
The issue is particularly serious where signed documents are checked automatically by companies or public bodies rather than reviewed carefully by an individual, Critical Security said.
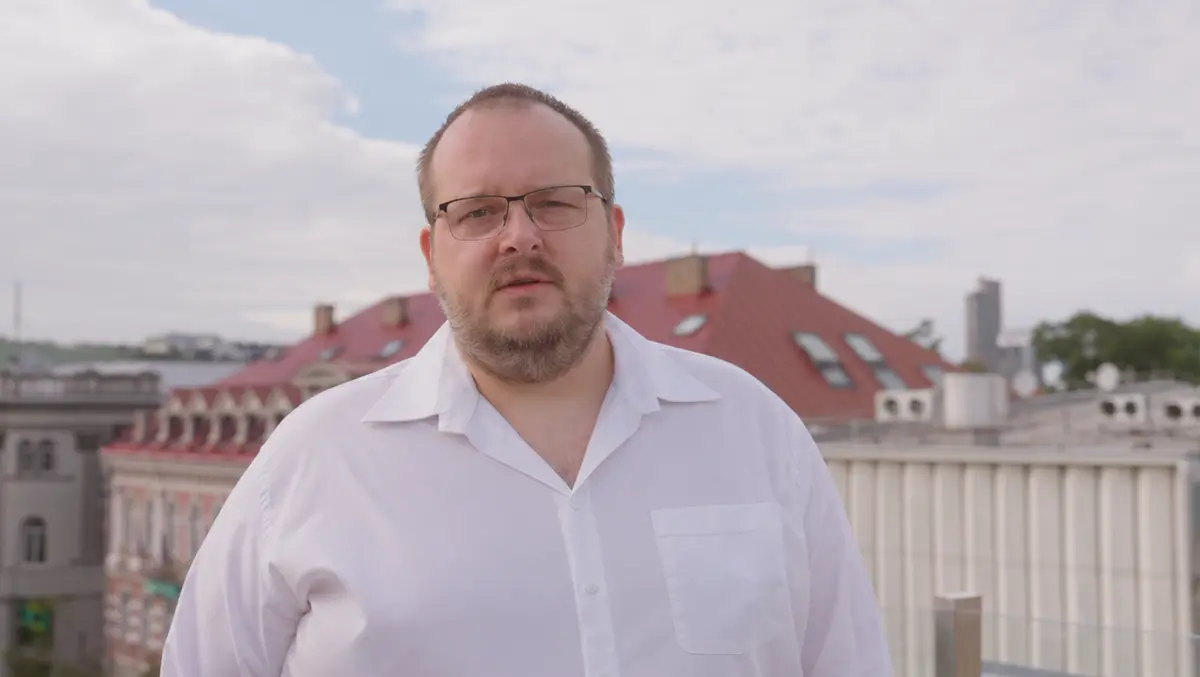
"Users shouldn't have to read a technical report and work out for themselves which part of a document is signed. If the verification system shows that there is a valid signature, individuals can be forced to take on obligations that they never agreed to. This threatens people's personal finances and even national security, for example through a forged power of attorney at a state institution," said Miroslav Lučinskij, Chief Executive Officer of Critical Security.
Wider Risk
The finding may have implications beyond the Baltics because PDF signatures use the same PAdES standard across the European Union. Under the eIDAS regulation, member states must recognise one another's qualified signatures, raising the possibility that validators in other countries may share the same weakness.
The question carries added weight as European states expand digital identity systems. Citizens across the bloc are due to receive Digital Identity Wallets that can create legally binding electronic signatures, increasing the volume of documents likely to be processed through validation software.
Critical Security said it is not aware of the flaw being exploited in the wild. Until fixes are introduced, it advises people receiving signed documents to check that the page count and content match the original, and says organisations using automated checks should treat any document whose signature does not cover the full file as unverified.
"A warning about content changed after signing has to be clear and visible immediately," said Lučinskij.
"The Baltics run some of Europe's most advanced digital public services in a region under constant hybrid warfare pressure, so flaws here carry real security weight," said Lučinskij. "But these systems are built on the same European standards as everyone else's. We found this problem where we looked. For any validator nobody has examined yet, the flaw may be a zero-day vulnerability the vendor doesn't know about."