

Keeper launches Google Chat tool for access approvals
Fri, 25th Sep 2026 (Today)
Keeper Security has launched a Google Chat integration for privileged access requests and approvals, extending its identity governance tools into Google Workspace environments.
The integration lets users request access, approve requests and retrieve credentials from within Google Chat. It also supports secrets management and just-in-time elevation requests, without requiring staff to switch to separate administrative tools.
Google Workspace is used by more than 9 million paying organisations worldwide, making collaboration software an important control point for identity and access management vendors. The launch reflects a broader push by security suppliers to embed approval and authentication steps in everyday workplace software rather than separate consoles.
The new Google Chat app is aimed at organisations that use Google Workspace as their main collaboration platform. It allows administrators to set time-limited access windows, apply approval-routing policies, and maintain audit trails and reporting tied to access decisions.
Embedded controls
Teams can submit vault access requests with justifications and custom permission levels through the chat interface. The integration also supports approval flows for endpoint privilege elevation and device approvals linked to federated authentication workflows.
Real-time notifications are sent to dedicated channels, allowing approvers to act in the same environment where operational discussions already take place. Audit logs for access requests, approvals and credential retrieval remain centralised.
At the technical level, the Google Chat app runs on an organisation's existing infrastructure using Commander Service Mode. Credentials remain encrypted end to end and do not pass through external services.
The approach is intended to reduce the operational burden of switching between collaboration tools and access management systems while maintaining tight control over privileged credentials. Privileged access remains a high-priority issue for security teams because administrator accounts and secrets are frequent targets in cyber attacks.
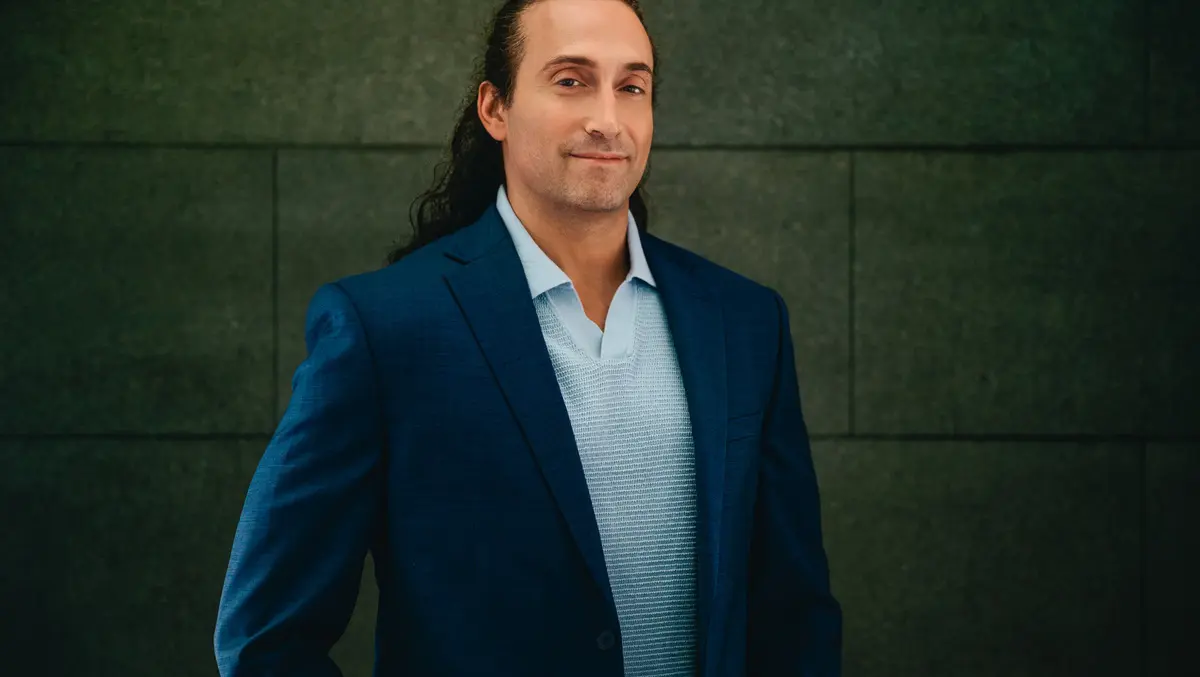
Craig Lurey, Chief Technology Officer and Co-founder of Keeper Security, said the goal is to place access controls directly inside collaboration software.
"Organisations need access controls embedded in the tools their teams already use," said Craig Lurey, Chief Technology Officer and Co-founder, Keeper Security.
He said the integration keeps encryption and system separation intact.
"Using this integration means your infrastructure stays isolated because the chat app is just the interface. The encryption and verification happen entirely in your environment, so credentials never exist in transit, whether to Google's infrastructure or ours," said Lurey.
Available now
The integration is available immediately for customers with active Keeper Secrets Manager or KeeperPAM licences. Setup is handled through a guided installation process that uses Keeper Secrets Manager to store configuration details and credentials.
The release gives Keeper another route to expand use of its privileged access and secrets management products within existing workplace platforms. Security vendors have increasingly sought tighter links with messaging and collaboration systems as companies try to reduce friction in approval workflows, especially for staff handling infrastructure, cloud systems and sensitive internal applications.
For administrators, the practical appeal is reducing manual hand-offs in access control. Rather than distributing credentials directly or handling approval requests through email and separate portals, teams can route requests, validate need, apply temporary permissions and record the outcome in a single workflow.
That matters because delays in privileged access approvals can slow operational work, while weak controls can create openings for misuse or compromise. Bringing those actions into chat platforms may improve response times, but it also increases the importance of maintaining strong verification and audit records around who requested access, who approved it and what level of access was granted.
Keeper said its model keeps the chat application as an interface layer while encryption and verification remain inside the customer's own environment, so credentials never exist in transit to Google's infrastructure or Keeper's systems.