

Keeper Security has integrated its privileged access management platform with SailPoint's identity governance system, allowing SailPoint to manage access changes for Keeper users and resources.
The integration connects SailPoint's identity governance and administration platform directly to KeeperPAM through a software connector. It is designed to help organisations automate provisioning, deprovisioning and entitlement management for users, vaults and managed resources within Keeper.
Identity governance and privileged access management often sit in separate parts of a company's security stack. In practice, governance teams may define who should get access, while security teams still have to make those changes manually in a privileged access system.
That gap creates operational risks, particularly when staff change roles or leave an organisation. If access rights are not updated quickly, privileged credentials can remain available longer than intended, leaving companies exposed to misuse or control failures.
The new connector automates the transfer of access decisions from SailPoint into Keeper's platform. It can provision team memberships, shared folders, roles, nodes, records and administrative permissions based on entitlements set within SailPoint.
The setup also allows access certification reviews conducted in SailPoint to include privileged credentials and identities managed through Keeper, giving compliance and audit teams a more complete view of who holds access across both systems.
Closing the gap
The move reflects a broader push among cyber security suppliers to reduce the number of manual steps between identity controls and access enforcement. Companies have increasingly focused on identity as a point of weakness, especially as the number of human users, service accounts and other non-human identities has grown.
Keeper cited its own research from this year showing that 96% of senior IT leaders believe disconnected security tools are creating exploitable gaps. It also reported that 64% do not yet operate with fully consolidated privileged access governance.
Credentials remain hidden from SailPoint during the process, preserving Keeper's zero-knowledge design. Grants, updates and revocations are also logged automatically across both platforms, which could help organisations track changes for security and compliance purposes.
For organisations in regulated sectors, the integration is also intended to ease audit preparation. Keeper said federal agencies can use the setup to support compliance with requirements covering account management, least-privilege enforcement and control of privileged credentials.
Keeper also highlighted its certifications and validation status, including FedRAMP High certification, FIPS 140-3 validation and inclusion on the Cybersecurity and Infrastructure Security Agency's Continuous Diagnostics and Mitigation Approved Products List. Those credentials may make the joint setup more relevant to public sector buyers and contractors working to strict security baselines.
Identity focus
The partnership underlines how identity governance providers and privileged access specialists are moving closer together as customers seek tighter operational links between policy and enforcement. Rather than relying on separate reviews and manual updates, organisations are trying to tie approval workflows directly to the systems that store and control sensitive credentials.
Keeper positions its platform around securing access for both human and non-human identities. Its broader product set includes password and passkey management, secrets management, privileged session management and endpoint privilege management.
SailPoint is widely used by organisations to manage identity governance, including approvals, certifications and policy controls around who should have access to which systems. Connecting that governance layer to privileged access tools can reduce the reconciliation work that previously sat between the two products.
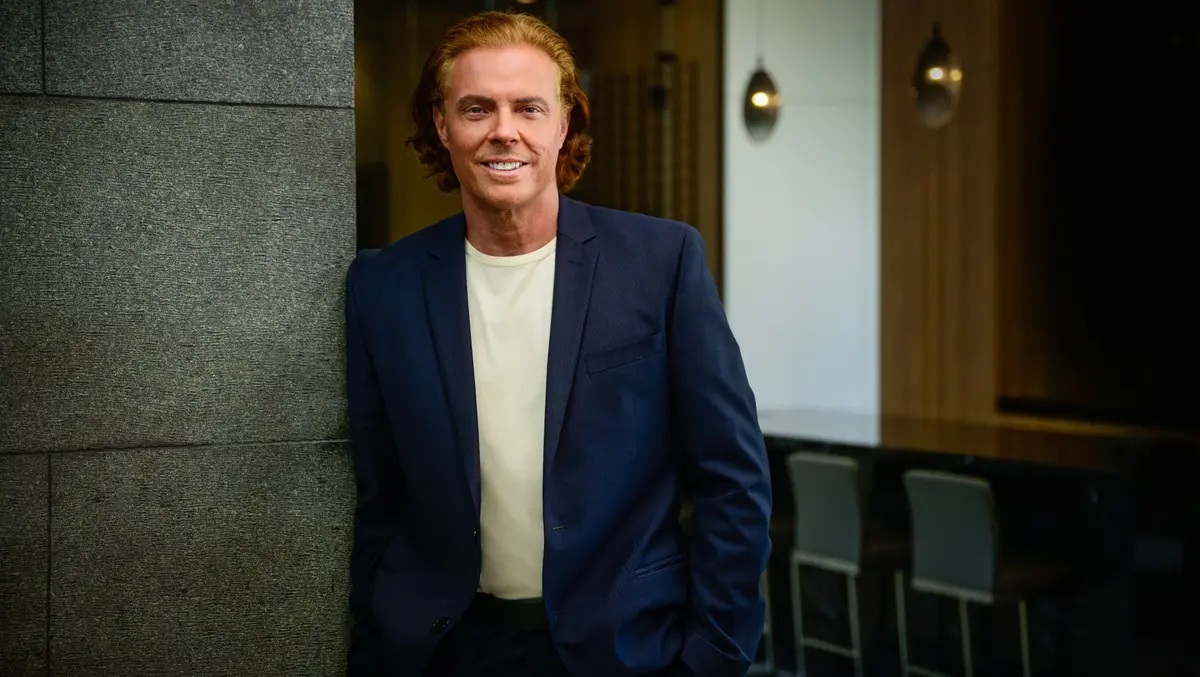
In a statement, Darren Guccione, Chief Executive Officer and Co-founder of Keeper Security, outlined the rationale for the integration.
"The organisations that properly implement identity security understand that governance is only as strong as its enforcement," Guccione said.
He added: "Seamless integration between IGA and PAM covering any type of human and non-human identity is an enormous gap for most enterprises. Our integration with SailPoint solves this."
The integration is available now for organisations using SailPoint for identity governance and KeeperPAM for privileged access management.