
Landmark invests €500,000 in managed compliance service
Wed, 28th Oct 2026 (Today)
Landmark is investing €500,000 to launch a managed compliance service, a move the Irish IT and cybersecurity provider said supports its target of 30% annual revenue growth.
The service is designed to help businesses meet and maintain compliance requirements including NIS2, DORA and ISO 27001. It also covers governance and policy work around the use of AI tools and the handling of company data.
The investment will fund development of the compliance offering through recruitment and training, including five new specialist roles across technical implementation, compliance and administration.
Landmark is positioning the service as a single source of support for organisations facing growing cybersecurity and governance demands. Customers are often under pressure to meet regulatory and commercial requirements without enough in-house expertise to manage the work.
That pressure is not limited to formal regulation. Businesses are also being asked to show evidence of compliance when bidding for contracts or seeking to join larger supply chains, adding another layer of scrutiny from customers, insurers and partners.
Growing demand
Landmark already supports businesses in Ireland with cybersecurity compliance work and says demand has risen as oversight has increased. It expects compliance to become a larger part of its business and plans to build the service into a dedicated division.
The managed service combines technical cybersecurity work with governance, policies and documentation. The aim is to reduce the need for companies to coordinate several advisers or suppliers while working towards compliance.
Requirements such as NIS2 and DORA have added urgency for many organisations, particularly those operating in critical sectors or supplying larger groups. ISO 27001 remains a widely used benchmark for information security management, and businesses are increasingly being asked to show they can maintain standards over time rather than simply achieve them once.
The addition of AI governance reflects a separate compliance concern for many companies. As organisations introduce AI tools into day-to-day operations, questions around data handling, internal controls and formal policies have become part of wider governance discussions.
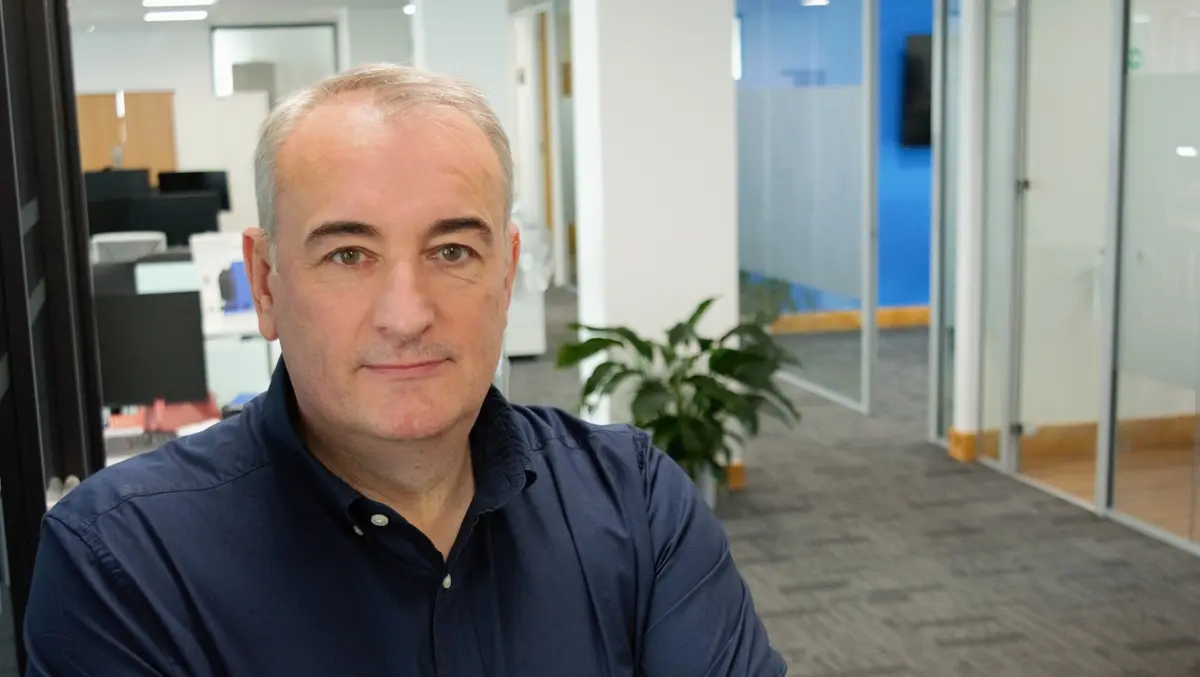
Ken Kelleher, Managing Director of Landmark, said: "Compliance is increasingly becoming a condition of doing business. Irish organisations are facing greater expectations from regulators, customers, insurers and supply-chain partners, and many simply don't have the specialist expertise in-house to keep pace with what is required.
"That is why we are launching this new managed compliance service and investing in the people, technology and training needed to deliver it.
"Achieving a standard is one thing; maintaining it is another. Businesses need the right technical controls in place, but they also need the policies, processes and governance behind them. Our approach is to bring those areas together and give customers the specialist support they need to stay compliant over time."
Founded in Dublin in 1998, Landmark provides IT and cybersecurity services to businesses in Ireland.
The investment points to a broader market trend, with compliance work moving closer to core IT and security operations as customers seek ongoing support rather than one-off certification projects.
Alongside the direct financial commitment, the creation of five specialist jobs suggests Landmark expects sustained demand rather than a short-term uptick. The new roles span operational delivery and back-office support, indicating the company is building the service as an ongoing line of business rather than a limited advisory offering.