

Whitepaper links water hacks to telecom cyber risk
Wed, 16th Sep 2026 (Today)
SureShield and BorderHawk have published a whitepaper linking recent attacks on US water systems to cyber risk in the telecommunications sector. It says 66% of the telecom operators analysed fall into an elevated risk band.
The paper draws on a broader telecom cybersecurity study of 3,106 operators from a pool of 7,320 identified through the Federal Communications Commission public registry. It argues that weaknesses seen in the water sector attacks, including unpatched known vulnerabilities, exposed management systems, and weak credential controls, are also common among smaller telecom providers.
CISA confirmed that hackers breached more than 100 internet-exposed water and wastewater systems across at least seven states, including Michigan and Minnesota. The campaign was widely attributed to Iran-linked actors targeting programmable logic controllers made by Rockwell, Schneider Electric, and Siemens.
According to the paper, some attackers used artificial intelligence tools to speed up reconnaissance and generate scripts aimed at specific Siemens PLC models. It warns that the same approach could be applied to telecom infrastructure that relies on outdated firmware, exposed administrative interfaces, and public-facing software with known vulnerabilities.
Shared weaknesses
The analysis argues that the overlap between the two sectors is structural rather than incidental. In the water attacks, internet-exposed operational technology and documented security flaws created openings for intruders. In telecom, the average operator in the study had 15 common vulnerabilities and exposures in its publicly visible attack surface.
The report also highlights basic email security gaps. It says 78% of operators in some states, including Maine, lacked DMARC records, which help prevent spoofing and phishing.
Researchers found that 41% of analysed operators had confirmed dark web exposure, including leaked credentials, stolen configurations, or compromised accounts. The paper says those conditions create a low-effort route for attackers, who can gain access without developing new exploits.
Resource constraints are another recurring theme. SureShield says 69% of US telecom operators have fewer than 50 employees, which it describes as a major barrier to maintaining traditional compliance and security programmes.
Sector dependence
The paper argues that telecom risk has wider implications because communications networks underpin other critical services. It lists emergency response, healthcare, financial systems, energy coordination, government operations, and transport logistics among the services that rely on telecom links.
That dependence means disruption in telecom could compound the impact of an attack on another sector. In a water treatment incident, alerts to first responders, public warnings, and coordination between agencies all depend on communications infrastructure.
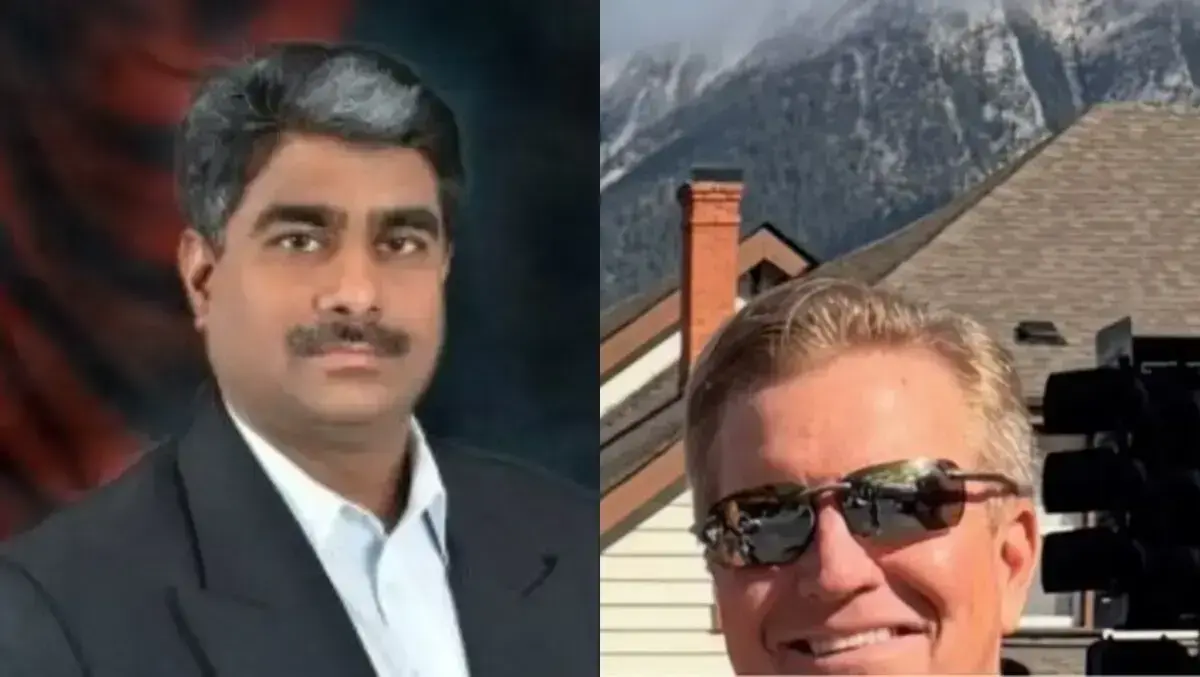
"When critical national infrastructure like telecommunication services is at risk of compromise or unable to operate securely, everything downstream that depends on it is at risk too, and can face significant disruption," said Jay Harmon, Chief Executive Officer, BorderHawk.
The document cites the National Institute of Standards and Technology Cybersecurity Framework and CISA's resilience strategy as recognising cascading failure across interdependent sectors as a central risk. It places telecom near the centre of those dependency chains.
Compliance gap
SureShield and BorderHawk argue that the main issue is not a lack of guidance. CISA advisories, NIST CSF 2.0, and Federal Communications Commission cybersecurity guidance are already available, but many operators lack the staff and tools to apply them continuously.
Their proposed answer is what they call continuous audit readiness: maintaining a live picture of compliance and risk rather than preparing evidence only when an audit approaches. In practice, that includes tracking vulnerabilities against CISA's Known Exploited Vulnerabilities catalogue, monitoring leaked credentials, and keeping control documentation current.
"Our objective with the 2026 Telco Report was to give the industry a mirror, to show, with verifiable data, what adversaries already know about their attack surfaces. The gap between what defenders can see and what attackers can enumerate is wide, and it's widening," said Chandrasekhar Bilugu, Chief Technology Officer, SureShield.
The paper sets out a 90-day roadmap for operators. Early steps include auditing internet-facing management interfaces, cross-checking software and firmware against the KEV catalogue, and implementing DMARC, DKIM, and SPF across organisational email domains.
It then recommends enabling logging across network infrastructure, scanning for leaked credentials on dark web markets, and reviewing third-party remote access. The final stage focuses on mapping controls against NIST CSF 2.0, automating evidence collection, and briefing boards on governance and risk findings.
"The combination of AI-assisted reconnaissance and the volume of unpatched, internet-exposed assets across the telecom sector creates a compounding risk. Operators can't manage what they can't see, and adversaries are increasingly seeing more than we are," said Sanjaya Kumar, Chief Executive Officer, SureShield.