
Qualys offers free help after PHP2Shell flaw disclosure
Mon, 26th Oct 2026 (Today)
Qualys is offering free services to help organisations identify and mitigate exposure to the PHP2Shell vulnerabilities. The offer covers up to 1,000 assets for 15 days.
The move follows disclosure of two critical PHP flaws, tracked as CVE-2026-109618 and CVE-2026-109619, both with CVSS v4.0 scores of 9.2. Attack traffic linked to the vulnerabilities has already been reported, and both bugs allow unauthenticated remote code execution.
According to Qualys, leaked PHP worker memory linked to the flaws can expose passwords, tokens and API keys. Although fixes have been issued for supported PHP branches, the Qualys Threat Research Unit said most deployments remain exposed because they are either vulnerable or running unsupported versions.
Data from more than 10,000 customers worldwide showed 167 million PHP package installations, 73% of them on internet-facing assets. That puts a large number of websites and systems within reach of remote attackers.
Among 156 million PHP package installations with a known version, only 28%, or 44 million, were vulnerable systems running supported PHP branches from 8.2 to 8.5, where a fix is available. Another 110 million installations, or 71%, were on end-of-life or end-of-support versions from PHP 5.4 to 8.1, where most systems are not expected to receive a vendor patch.
The same dataset showed that only 581,000 installations, or 0.37%, had been patched in the first 24 hours after disclosure. The figures point to a slow early remediation rate despite the severity of the flaws.
Exposure levels
The combination of internet-facing systems and outdated PHP versions has widened the immediate response challenge for security teams. For organisations that cannot quickly upgrade or patch PHP without affecting business systems, mitigation steps may be the faster option.
The free service includes access to products from the Qualys TruRisk Platform, including VMDR, Enterprise TruRisk Management and TruRisk Eliminate. The tools are designed to help security teams move from discovering vulnerable PHP instances to verifying that remediation steps have closed the exposure.
The process starts with discovery of vulnerable PHP instances, including those running in containers or bundled inside other applications. It then moves to prioritising internet-facing servers and older PHP versions, validating exploitability, patching supported releases, applying mitigations to unsupported versions and rescanning affected systems.
For older versions, the guidance includes using operating system vendor backports where available, or isolating systems and planning retirement where patches do not exist. That reflects the scale of the unsupported estate identified in Qualys research.
Vendor response
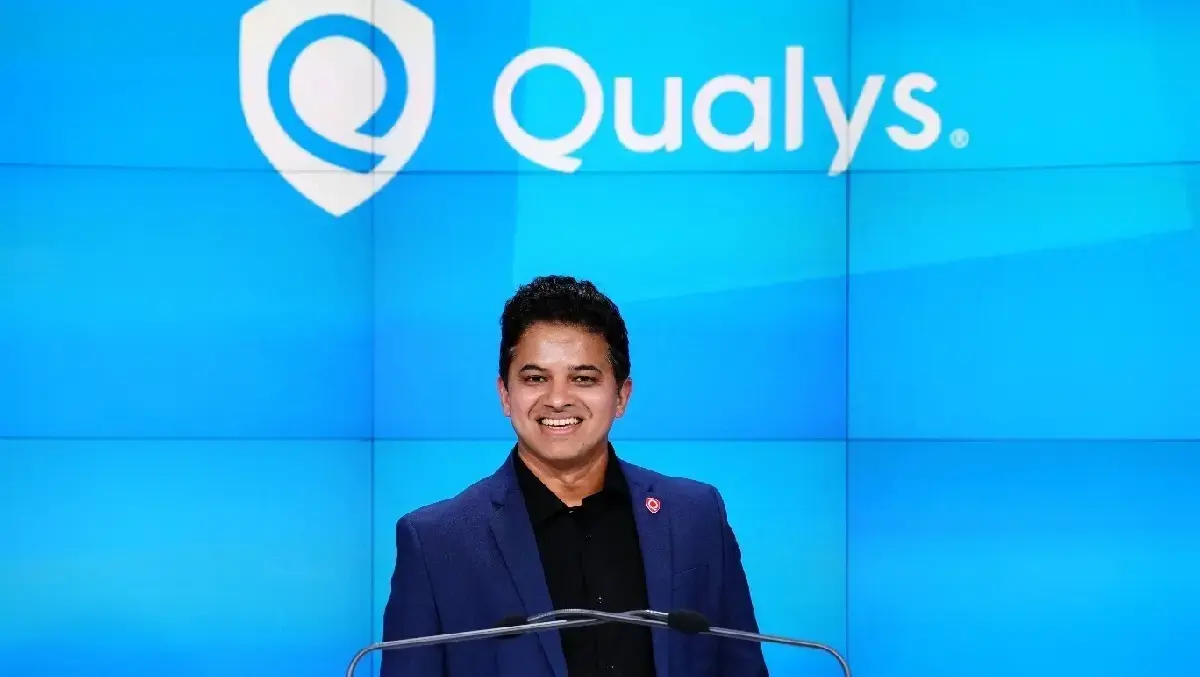
Shailesh Athalye, Chief Product Solutions Officer at Qualys, described the risk in direct terms.
"PHP2Shell puts a large share of the web at risk, and over 70% of installations will not have a patch," Athalye said.
He said organisations need immediate visibility into whether their systems are exposed and how to address the issue.
"With attackers already moving, security teams need to know right now whether they are exposed and how to fix it immediately. Qualys is making our services available so organisations can find, prioritise and close these exposures before they are exploited," Athalye said.