

Qomplio opens early access for EU compliance platform
Thu, 17th Sep 2026 (Today)
Qomplio has opened an early access programme for its compliance platform and begun onboarding its first pilot customers in Europe.
The move comes as businesses across the European Union face overlapping compliance demands under the AI Act, GDPR and NIS2, with the Data Act and the Cyber Resilience Act also approaching.
Founded in 2025, Qomplio is focused on a specific problem in European regulation: obligations under one law can trigger additional duties under another. Many organisations still treat each framework separately, even when the same system or incident creates parallel reporting, assessment and documentation requirements.
One example is the use of AI systems that process personal data. In that case, a business may need to complete both a Data Protection Impact Assessment under GDPR and a Fundamental Rights Impact Assessment under the AI Act, with each process carrying separate evidence and approval requirements.
A cyber incident can create a similar burden. A ransomware attack involving customer data may trigger notification duties under both NIS2 and GDPR, each with different reporting routes and time limits.
Regulatory overlap
Qomplio's platform is designed to identify links across frameworks as they arise and carry evidence from one assessment into another. It uses a rules-based approach to map obligations and present what it describes as explainable scoring, while keeping human sign-off at each stage.
The regulatory position is also shifting. A revision to the EU AI Act published in July 2026 changed the enforcement timeline for some of the law's most demanding high-risk provisions, while leaving transparency rules and AI literacy duties in place.
That staggered adjustment has made it harder for companies to track which obligations apply and when, particularly when systems fall under several regimes at once. In practice, legal, security and product teams may keep separate registers and records, creating gaps between assessments and reporting cycles.
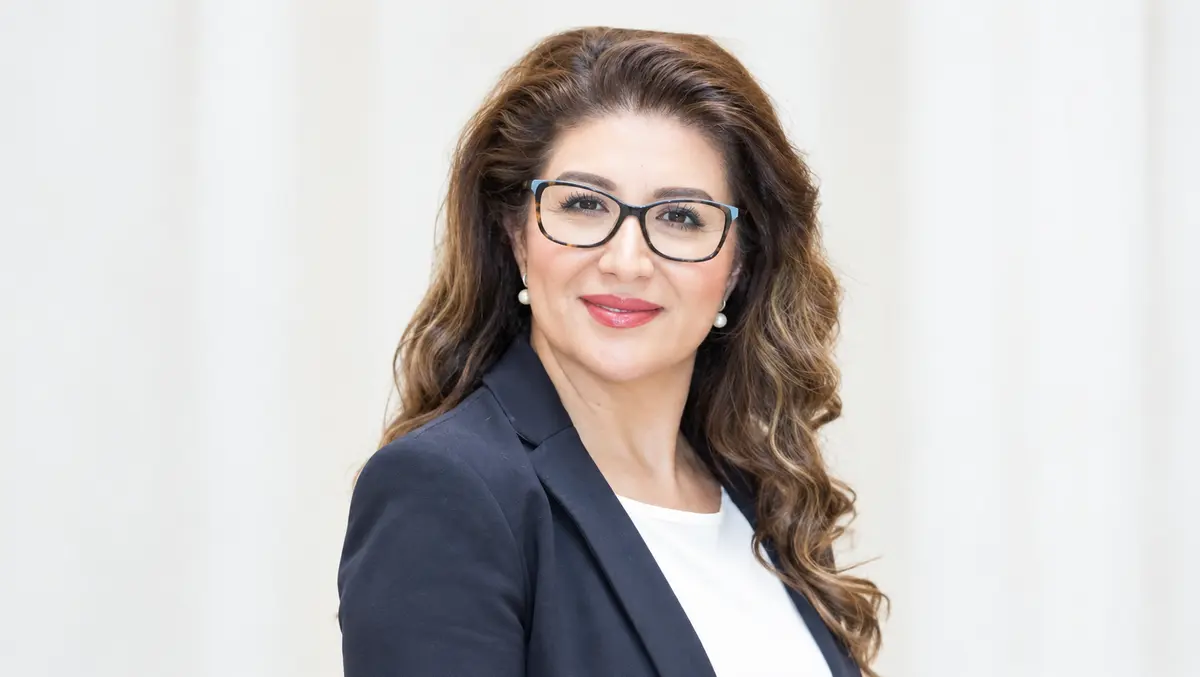
Chief Executive Officer Azin Ahlgren said the recent AI Act changes showed the limits of manual compliance processes. "The AI Act revision published in July is a good example of why point-in-time compliance does not work. By August, the obligations had changed. Companies managing this manually are always one amendment behind, and most will not know until they are already exposed," Ahlgren said.
Commercial pressure
Qomplio also links the issue to procurement. Businesses are increasingly being asked to show a verified and auditable compliance position during commercial discussions, not only when dealing with regulators, according to the company.
That reflects a broader shift in Europe, where buyers, partners and larger corporate customers are asking suppliers to show how they handle data, cyber risk and AI governance. For smaller and mid-sized companies, those checks can create a burden similar to formal regulatory audits.
Ahlgren said data location and control are part of the compliance picture. "Where your compliance data lives and who has jurisdiction over it is itself a compliance question," she said. "Qomplio is founded on EU-native infrastructure, built for European regulation, from day one."
Founding team
Ahlgren founded the company after a career spanning software development, solution architecture and delivery leadership in regulated sectors including healthcare, aviation and manufacturing. Her previous roles included positions at Siemens Medical Solutions, Extenda, Boeing and SKF.
The wider founding team includes Chief Technology Officer Danni Efraim, Chief Product Officer Christian Svalander and Chief Marketing Officer Povel Torudd. Qomplio says it has built the platform so that regulatory sources, AI automation and human accountability remain separate.
Under that model, obligations are assessed across applicable frameworks using a deterministic rules engine rather than open-ended generative outputs. Each AI system within the platform produces a locked and versioned evidence file intended to support audit and regulatory review, according to the company.
Qomplio's current coverage includes the AI Act, GDPR and NIS2. It plans to add the Data Act and the Cyber Resilience Act, reflecting the growing range of digital regulation facing European businesses.
For companies trying to navigate those rules, the challenge is no longer limited to understanding one law at a time. It increasingly lies in managing the points where separate frameworks meet, overlap and change.